For companies
Document the incident from minute one
Internal fraud, data leaks, policy breaches — with a verifiable chain of custody, without waiting for an external examiner to start documenting.
The problem
Why improvising gets expensive later
An internal investigation needs neutrality
If the same person investigating also collects and holds the evidence, it's harder to defend if the case escalates.
An external expert isn't always there from minute one
The incident is happening now; documenting it properly shouldn't wait until someone external arrives on site.
Knowing who accessed the evidence afterwards matters too
A read audit log records who viewed or downloaded each piece of evidence, and from where.
How it's used
Two capture paths, one shared access log
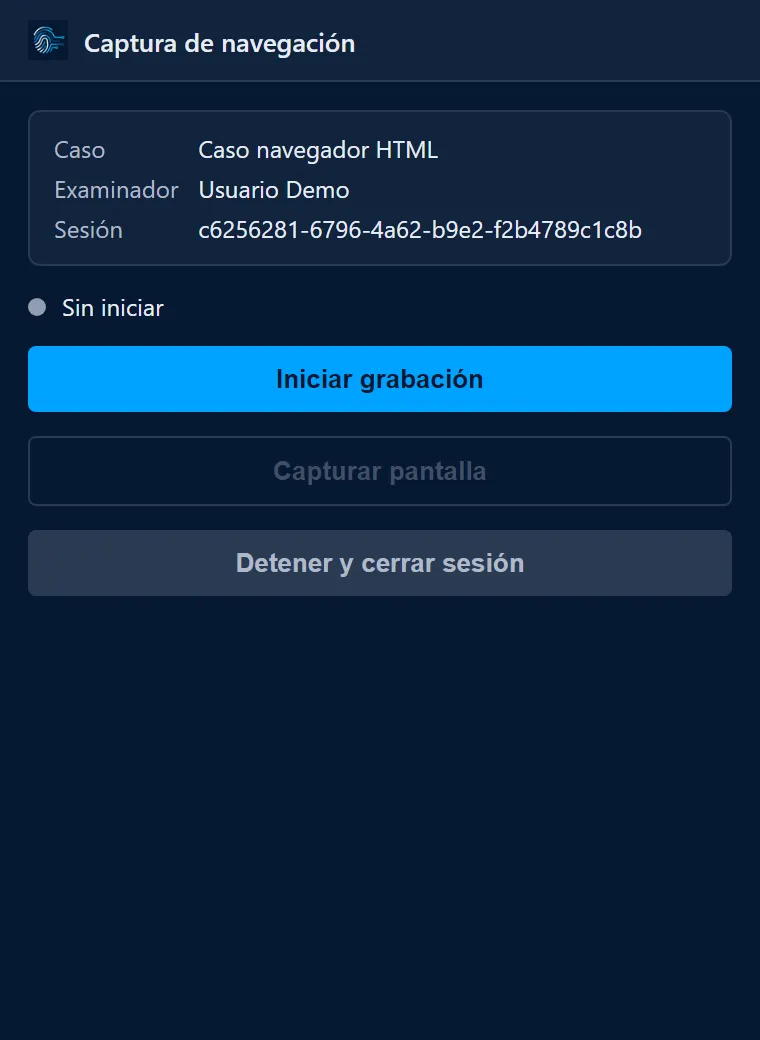
Browser extension
For investigations that start on a website, a webmail client or a social network — records the session without stealing focus from the examined tab.
Desktop client
For extractions on corporate machines, with the same hash-and-timestamp mechanism an external examiner would use.
Read audit log
Every access to or download of already-accepted evidence is logged — who, when, and from where.
Let's start
Get ready before the next incident happens
We'll show you how it fits into your current response protocol.